
Recommended tools and plans
Choose the smallest plan that covers the specific workflow and its limiting resource.
For recurring public-site checks
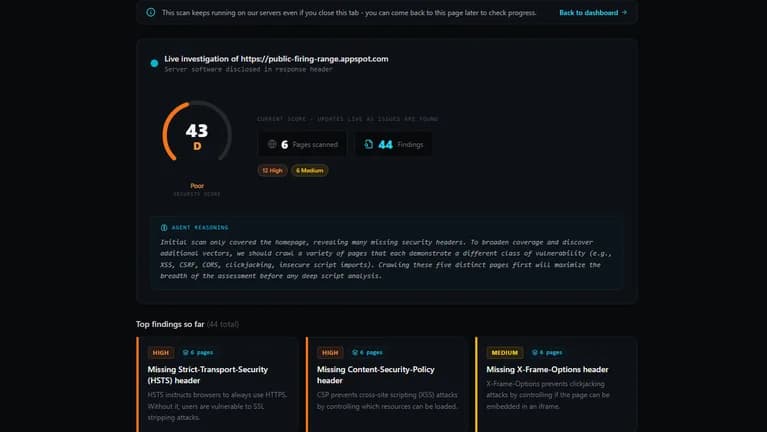
Decloak
$49 covers fifty pages per scan and five scans per domain per day.
Keep in mind: No active testing or authenticated mode; findings still need review.
Buy nowExplore Decloak’s features and plansFor an assistant-led scan and fix workflow

Vibe App Scanner
$119 includes MCP and current separate repository allowances.
Keep in mind: REST API requires Tier 3; repository operations are not yet available through the website API.
Buy nowExplore Vibe App Scanner’s features and plansDefine the required evidence
Start with the application paths that matter: login, ordinary-user access, administrative actions and public data. A tool that sees the homepage may not assess records behind authentication or business rules enforced by a backend. Identify what remains unassessed rather than interpreting missing findings as a pass.
A client requirement for a professional penetration test is different from recurring automated hygiene checks. Neither product should be represented as automatically fulfilling every contractual security assessment.
Understand the quota model
Decloak uses daily per-domain limits and a page ceiling. This can fit repeated small verification cycles, but larger sites need attention to the routes actually reached. Enterprise adds testing capabilities rather than unlimited crawl depth.
Vibe App Scanner uses a monthly website-scan pool. Three sites scanned four times consume twelve runs before remediation checks. Its unlimited website slots on Tier 3 still share one monthly pool, and repository scans have separate targets and allowances.
Check the integration you actually need
Vibe App Scanner includes MCP from Tier 2 but REST API only on Tier 3. The founder says repository runs are not yet exposed through the public website-scan API/MCP workflow. Buying an API tier therefore does not establish automatic repository scans on every pull request.
Decloak Pro provides API access while Enterprise adds active and authenticated testing. Automate only a workflow whose scope and results you can verify; a scheduled task should report incomplete coverage as well as new findings.
Review before applying fixes
Read the affected URL, evidence and proposed remediation. A header warning, dependency advisory and access-control defect have different consequences. Ask a coding assistant to verify applicability and produce a small reviewable change, then test the affected user journey.
Buyer feedback for both tools includes requests for clearer reports or better coverage context. Use those buyer reports to guide your evaluation. Keep evidence for accepted findings and document why a false positive was dismissed.
Protect the testing boundary
Use only authorized systems and agree on active-test conditions. If an interactive firewall prevents a scan, a representative staging environment may help without weakening production protection; production-specific configuration still needs separate review.
Private repository analysis introduces code-handling and retention questions. Confirm the actual provider access, temporary source handling and report retention before uploading client code. A free scan can demonstrate presentation but does not prove the paid tier’s complete entitlements.
Feature comparison
Use the same checklist for each tool. Plan limits, paid extras and features that need confirmation are shown separately.
Features are grouped by documented coverage. “Not confirmed” means the evidence is incomplete, not that a feature is absent.
Check each product’s plan notes for tier limits and additional costs. Feature coverage is not a quality rating.
Buying questions
Does a clean scan prove an app safe?
No. Coverage, unsupported frameworks and business logic still require review.
Which tool has repository scanning?
Vibe App Scanner currently offers higher-tier repository beta allowances with specific limitations.
Which Decloak tier includes active testing?
Enterprise; Pro API access does not itself include active testing.